Category Archives: Global Analysis

A Geographical Breakdown of What’s Going on in the World

Event Invite: DC Happy Hour on Framing Chinese SCS Activity

By Scott Cheney-Peters

Join CIMSEC’s DC chapter as it bookends the 7th CSIS Conference on the South China Sea with Dr. Alessio Patalano, Reader in War Studies, King’s College London, for its July meet-up and a lively informal discussion on Chinese maritime coercion and the validity of the concepts of hybrid warfare and grey zones.  Other surprise guests are expected to drop by…

Time: Tuesday, 18 July, 5:30-7:30pm

Place: The Commissary,  1443 P St NW, Washington, DC

RSVPs not necessary.

Beijing’s Views on Norms in Cyberspace and Cyber Warfare Strategy Pt. 2

By LCDR Jake Bebber USN

The following is a two-part series looking at PRC use of cyberspace operations in pursuit of its national strategies and the establishment of the Strategic Support Force. Part 1 considered the centrality of information operations and information war to the PRC’s approach toward its current struggle against the U.S. Part 2 looks at the PRC’s use of international norms and institutions in cyberspace, and possible U.S. responses.

Cyber-Enabled Public Opinion and Political Warfare

Many American planners are carefully considering scenarios such as China making a play to force the integration of Taiwan, seize the Senkaku Islands from Japan, or seize and project power from any and all claimed reefs and islands in the South China Sea. Under these scenarios we can expect preemptive strikes in the space and network domains in an attempt to “blind” or confuse American and allied understanding and establish a fait accompli. This will, in Chinese thinking, force the National Command Authority to consider a long and difficult campaign in order to eject Chinese forces, and the CCP is placing a bet that American decision makers will choose to reach a political accommodation that recognizes the new “facts on the ground” rather than risk a wider military and economic confrontation.

The role of public opinion warfare may be an integral component of future crisis and conflict in Asia. Well in advance of any potential confrontation, Chinese writing emphasizes the role of “political warfare” and “public opinion warfare” as an offensive deterrence strategy. China will seek to actively shape American, allied, and world opinion to legitimize any military action the CCP deems necessary. We might see cyber-enabled means to “incessantly disseminate false and confused information to the enemy side … through elaborate planning [in peacetime], and [thereby] interfere with and disrupt the enemy side’s perception, thinking, willpower and judgment, so that it will generate erroneous determination and measures.”1 China may try to leverage large populations of Chinese nationals and those of Chinese heritage living outside China as a way to influence other countries and generate new narratives that promote the PRC’s position. Consider, for example, how Chinese social media campaigns led to the boycotts of bananas from the Philippines when it seized Scarborough Reef, or similar campaigns against Japanese-made cars during its ongoing territorial dispute over the Senkaku Islands. Most recently, Lotte Duty Free, a South Korean company, suffered distributed denial-of-service attacks from Chinese IP servers – almost certainly a response to South Korea’s recent decision to host the THAAD missile defense system.

It is also critical to recognize China’s understanding and leverage of the American political, information, and economic system. Over decades, China has intertwined its interests and money with American universities, research institutes, corporate institutions, media and entertainment, political lobbying, and special interest organizations. This has had the effect of co-opting a number of institutions and elite opinion makers who view any competition or conflict with China as, at best, detrimental to American interests, and at worst, as a hopeless cause, some going so far as to suggest that it is better for the U.S. to recognize Chinese primacy and hegemony, at least in Asia, if not worldwide. Either way, China will maximize attempts to use cyber-enabled means to shape American and world understanding so as to paint China as the “victim” in any scenario, being “forced” into action by American or Western “interference” or “provocation.”

What can the U.S. do to Enhance Network Resilience?

One of the most important ways that network resiliency can be addressed is by fundamentally changing the intellectual and conceptual approach to critical networks. Richard Harknett, the former scholar-in-residence at U.S. Cyber Command, has suggested a better approach. In a recent issue of the Journal of Information Warfare, he points out that cyberspace is not a deterrence space, but an offense-persistent environment. By that he means that it is an inherently active, iterative, and adaptive domain. Norms are not established by seeking to impose an understood order (such as at Bretton Woods) or through a “doctrine of restraint,” but rather through the regular and constant interactions between states and other actors.  Defense and resiliency are possible in this space, but attrition is not. Conflict here cannot be contained to “areas of hostility” or “military exclusion zones.” No steady state can exist here—every defense is a new opportunity for offense, and every offense generates a new defense.2

Second, the policy and legal approach to network resiliency must shift from a law enforcement paradigm to a national security paradigm. This paradigm is important because it affects the framework under which operations are conducted. The emphasis becomes one of active defense, adaptation, identification of vulnerabilities and systemic redundancy and resilience. A national security approach would also be better suited for mobilizing a whole-of-nation response in which the government, industry, and the population are engaged as active participants in network defense and resiliency. Important to this is the development of partnership mechanisms and professional networking that permit rapid sharing of information at the lowest level possible. Major telecommunications firms, which provide the infrastructure backbone of critical networks, require timely, actionable information in order to respond to malicious threats. Engagement with the private sector must be conducted in the same way they engage with each other – by developing personal trust and providing actionable information.

Network hardening must be coupled with the capabilities needed to rapidly reconstitute critical networks and the resiliency to fight through network attack. This includes the development of alternative command, control, and communication capabilities. In this regard, the military and government can look to industries such as online retail, online streaming, and online financial networks (among others) that operate under constant attack on an hourly basis while proving capable of providing on-demand service to customers without interruption. Some lessons might be learned here.    

Third, new operational concepts must emphasize persistent engagement over static defense. The United States must have the capacity to contest and counter the cyber capabilities of its adversaries and the intelligence capacity to anticipate vulnerabilities so we move away from a reactive approach to cyber incidents and instead position ourselves to find security through retaining the initiative across the spectrum of resiliency and active defensive and offensive cyber operations.

Congressional Action and Implementing a Whole-of-Government Approach

There are five “big hammers” that Congress and the federal government have at their disposal to effect large changes – these are known as the “Rishikof of Big 5” after Harvey Rishikof, Chairman of the Standing Committee on Law and National Security for the American Bar Association. These “hammers” include the tax code and budget, the regulatory code, insurance premiums, litigation, and international treaties. A comprehensive, whole-of-nation response to the challenge China represents to the American-led international system will require a mixture of these “big hammers.” No one change or alteration in Department of Defense policy toward cyberspace operations will have nearly the impact as these “hammers.”3

The tax code and budget, coupled with regulation, can be structured to incentivize network resiliency and security by default (cyber security built into software and hardware as a priority standard), not only among key critical infrastructure industries, but among the population as a whole to include the telecommunication Internet border gateways, small-to-medium sized Internet service providers, and information technology suppliers. Since the federal government, Defense Department, and Homeland Security rely largely on private industry and third-party suppliers for communications and information technology, this would have the attendant effect of improving the systems used by those supporting national security and homeland defense. The key question then is: how can Congress incentivize network resiliency and security standards, to include protecting the supply chain, most especially for those in industry who provide goods and services to the government?

If the tax code, budget, and regulation might provide some incentive (“carrots”), so too can they provide “sticks.” Litigation and insurance premiums can also provide similar effects, both to incentivize standards and practices and discourage poor cyber hygiene and lax network security practices. Again, Congress must balance the “carrots” and “sticks” within a national security framework.

Congress might also address law and policy which permits adversary states to leverage the American system to our detriment. Today, American universities and research institutions are training China’s future leaders in information technology, artificial intelligence, autonomous systems, computer science, cryptology, directed energy and quantum mechanics. Most of these students will likely return to China to put their services to work for the Chinese government and military, designing systems to defeat us. American companies hire and train Chinese technology engineers, and have established research institutes in China.4 The American taxpayer is helping fund the growth and development of China’s military and strategic cyber forces as well as growth in China’s information technology industry.

Related specifically to the Department of Defense, Congress should work with the Department to identify ways in which the services man, train, and equip cyber mission forces. It will have to provide new tools that the services can leverage to identify and recruit talented men and women, and ensure that the nation can benefit long-term by setting up appropriate incentives to retain and promote the best and brightest. It will have to address an acquisition system structured around platforms and long-term programs of record. The current military is one where highly advanced systems have to be made to work with legacy systems and cobbled together with commercial, off-the-shelf technology. This is less than optimal and creates hidden vulnerabilities in these systems, risking cascading mission failure and putting lives in jeopardy.

Finally, Congress, the Department of Defense, and the broader intelligence and homeland security communities can work together to establish a center of excellence for the information and cyber domain that can provide the detailed system-of-systems analysis, analytic tools, and capability development necessary to operate and defend in this space. Such centers have been established in other domains, such as land (e.g., National Geospatial Intelligence Agency), sea (e.g., Office of Naval Intelligence) and air and space (e.g., National Air and Space Intelligence Center).

Conclusion

It is important to understand that this competition is not limited to “DOD versus PLA.” The U.S. must evaluate how it is postured as a nation is whether it is prepared fight and defend its information space, to include critical infrastructure, networks, strategic resources, economic arrangements, and the industries that mold and shape public understanding, attitude, and opinion. It must decide whether defense of the information space and the homeland is a matter of national security or one of law enforcement, because each path is governed by very different approaches to rules, roles, policies, and responses. Policymakers should consider how to best address the need to provide critical indications, warnings, threat detection, as well as the system-of-systems network intelligence required for the U.S. to develop the capabilities necessary to operate in and through cyberspace. For all other domains in which the U.S. operates, there is a lead intelligence agency devoted to that space (Office of Naval Intelligence for the maritime domain, National Air and Space Intelligence Center for the air and space domains, etc.).

It must always be remembered that for China, this is a zero-sum competition – there will be a distinct winner and loser. It intends to be that winner, and it believes that the longer it can mask the true nature of that competition and keep America wedded to its own view of the competition as a positive-sum game, it will enjoy significant leverage within the American-led system and retain strategic advantage. China is pursuing successfully, so far, a very clever strategy of working through the system the U.S. built in order to supplant it – and much of it is happening openly and in full view. This strategy can be countered in many ways, but first the U.S. must recognize its approach and decide to act.

LCDR Jake Bebber is a cryptologic warfare officer assigned to the staff of Carrier Strike Group 12. He previously served on the staff of U.S. Cyber Command from 2013 – 2017. LCDR Bebber holds a Ph.D. in public policy. He welcomes your comments at: jbebber@gmail.com. These views are his alone and do not necessarily represent any U.S. government department or agency.

1. Deal 2014.

2. Richard Harknett and Emily Goldman (2016) “The Search for Cyber Fundamentals.” Journal of Information Warfare. Vol. 15 No. 2.

3. Harvey Rishikof (2017) Personal communication, April 21.

4. See: https://www.bloomberg.com/view/articles/2013-03-28/chinese-hacking-is-made-in-the-u-s-a-

Featured Image: Nokia Security Center server room (Photo: Nokia)

Latin American Navies and Antarctica

The Southern Tide

Written by W. Alejandro Sanchez, The Southern Tide addresses maritime security issues throughout Latin America and the Caribbean. It discusses the challenges regional navies face including limited defense budgets, inter-state tensions, and transnational crimes. It also examines how these challenges influence current and future defense strategies, platform acquisitions, and relations with global powers.

“The security environment in Latin America and the Caribbean is characterized by complex, diverse, and non-traditional challenges to U.S. interests.” Admiral Kurt W. Tidd, Commander, U.S. Southern Command, before the 114th Congress Senate Armed Services Committee, 10 March 2016.

By W. Alejandro Sanchez and Brittney J. Figueroa

Latin American governments have a strong presence in Antarctica, with two countries, Argentina and Chile, formally claiming Antarctic territories while several others carry out annual scientific expeditions (apart from having research bases there). Regional navies are of paramount importance in these operations as they are the spearhead of their respective nations’ expeditions and security initiatives in Antarctic waters. In fact, in recent months, there have been new developments that signal a greater Latin American naval presence in the Antarctic in the near future: Peru has commissioned its new oceanographic vessel while Chile has commenced the construction of a new icebreaker.

Antarctic geopolitics will only increase in importance due to climate change and the upcoming year 2048 when the Antarctic Treaty will be open for review. Hence it is important that Latin America, broadly speaking, takes steps to maintain a continuous presence in Antarctica in order to have a voice when the frozen continent’s future is decided. Increasing budgets in order to modernize or replace aging vessels and expanding already successful scientific and security programs will play a critical role in regional navies’ future Antarctic operations.

Antarctica as a National Interest

The importance of Antarctica in Latin American security and defense strategies, as well as more comprehensive foreign policy concepts, cannot be overemphasized. One example of this is Antarctica’s frequent and prominent mentions in regional White Papers. For example, Argentina’s 2015 White Book repeatedly references Antarctica, and explains how “the Ministry of Defense considers of the upmost importance the upgrade [of military platforms] necessary for the scientific development, international cooperation and preservation of the Antarctic environment” (P. 43). Similarly Peru’s 2005 White Book mentions how the “Ministry of Defense, via the armed forces, has a fundamental role in the logistical support and the scientific research that encompasses the Peruvian presence in Antarctica” (P.42). Finally, Chile’s 2010 White Book has an extensive chapter on the Chilean Antarctic, explaining how the armed forces aim to “have a permanent presence, even during winter, in the Antarctic continent and its islands” and to carry out oceanographic scientific research in the region (P. 51 & 52).

These three different White Books exemplify Latin American nations’ interests in having a strong Antarctic presence and how militaries, particularly navies, are regarded as the tip of the spear of Antarctic operations.

Vessels and Patrols

Argentina and Chile possess several platforms that operate in Antarctic waters for expeditions, patrols, and to support their Antarctic bases. Argentina has the icebreaker ARA Almirante Irízar (Q5) and in 2014, Buenos Aires acquired four Russian Neftegaz-class multipurpose vessels to support its Antarctic bases. Meanwhile, Chile has the icebreaker Almirante Oscar Viel (AP46), and several other vessels capable of operating in Antarctic waters.

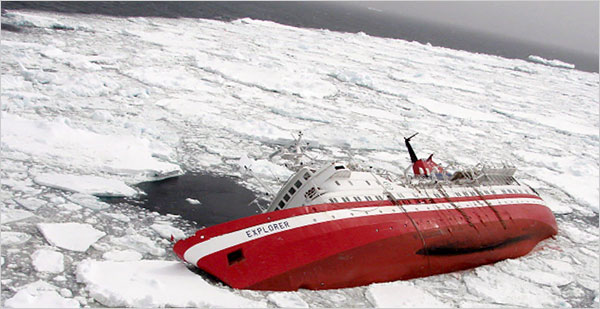
Additionally, the two countries set aside their differences—overlapping territorial claims in the Antarctic—to create the Joint Antarctic Naval Patrol (Patrulla Antártica Naval Combinada: PANC) in 1998. Via the PANC, naval platforms from the two countries come together during the Antarctic Summer months (November-March) to patrol Antarctic waters, assist vessels in need (e.g. the tourist vessel M/V Explorer in 2007), respond to oil spills, and visit and support various bases.

A picture taken by the Chilean Air Force shows the Explorer, which struck an iceberg in the Antarctic Ocean. (Fuerza Aerea de Chile via European Pressphoto Agency)

The PANC’s navies pride themselves on being prepared to safeguard the lives of those who work in and travel to the region, and are prepared for search and rescue missions along with other various emergencies at sea. The creation and success of the PANC should not be underestimated as it exemplifies the possibilities of collaborative naval efforts in the Antarctic. It is worth stressing that neither PANC country is a military power, and they do not have the same naval capabilities as some of their wealthier Antarctic counterparts, thus putting them at a great disadvantage (especially when considering each nation’s capabilities alone). However, despite the older vessels in their fleets, their partnership over the past two decades has proven to be effective both to patrol Antarctic waters, and also as a confidence-building mechanism.

Non-claimant nations also have important Antarctic programs. Peru, for example, recently received BAP Carrasco (BOP171), constructed by the Spanish Freire shipyard in 2016. Jane’s 360 explains that “the steel-hulled ship has a length of 95.9 m, a 6,000-tonne displacement, has a streamlined and raked superstructure with a meteorological sensor platform at the forward end,” which will be of great help for Peru’s future operations in the Antarctic. In addition, Brazil has a varied presence in the region that consists of the Almirante Maximiano (H-41), an ice breaker, the Ary Rongel (H-44), an oceanographic support ship, and several C-130 Brazilian Air Force (FAB) aircraft that are utilized to transport essential equipment and personnel to the Brazilian Antarctic Program (PROANTAR) facilities.

Regarding Chile, it has commenced the construction of a brand-new icebreaker as part of its Antarctica I project. Thanks to information provided to the authors by ASMAR, (Astilleros y Maestranzas de la Armada) Chile’s state-owned shipyard that has partnered with the Chilean Navy since 1895, we know that the new platform, an over $210 million project, will be capable of longer Antarctic missions in part due to its design which allows it to operate at temperatures as low as -30 Celsius. Additionally, the icebreaker will be equipped with modern, state-of-the-art scientific equipment in its microbiological and chemical laboratories. Construction commenced on 9 May at ASMAR’s Talcahuano facilities. The new vessel will be operational by the 2022-2023 season, and will greatly support Chile’s Antarctic operations.

As for Colombia, the navy has refitted one of its oceanic patrol vessels, ARC 20 de Julio (PZE-46), so it can better operate in Antarctic conditions. The vessel has already carried out two expeditions. 

Uruguay’s presence in Antarctica since 1985 is also worth noting. The ROU 26 Vanguardia is the small South American country’s primary platform used for scientific research and to support Base Artigas and Station Ruperto Elichiribehety. The Vanguardia, named Otto Von Guericke at the time of its construction, was built in Poland for East Germany in 1976. The vessel was purchased by Montevideo in 1991 and was then given its current name. It has a length of 72.62 m, displaces 1872 tons, and a maximum speed of 14.5 knots. Other ships that participate in the country’s Antarctic activities are ROU 04 Artigas and ROU 22 Oyarvide. Unlike the PANC, which focuses on patrolling and safety activities, Uruguay’s main operations in the continent take place via the Uruguayan Antarctic Institute, a national agency under the supervision of the Ministry of Defense that focuses on scientific, technological, and logistic activities.

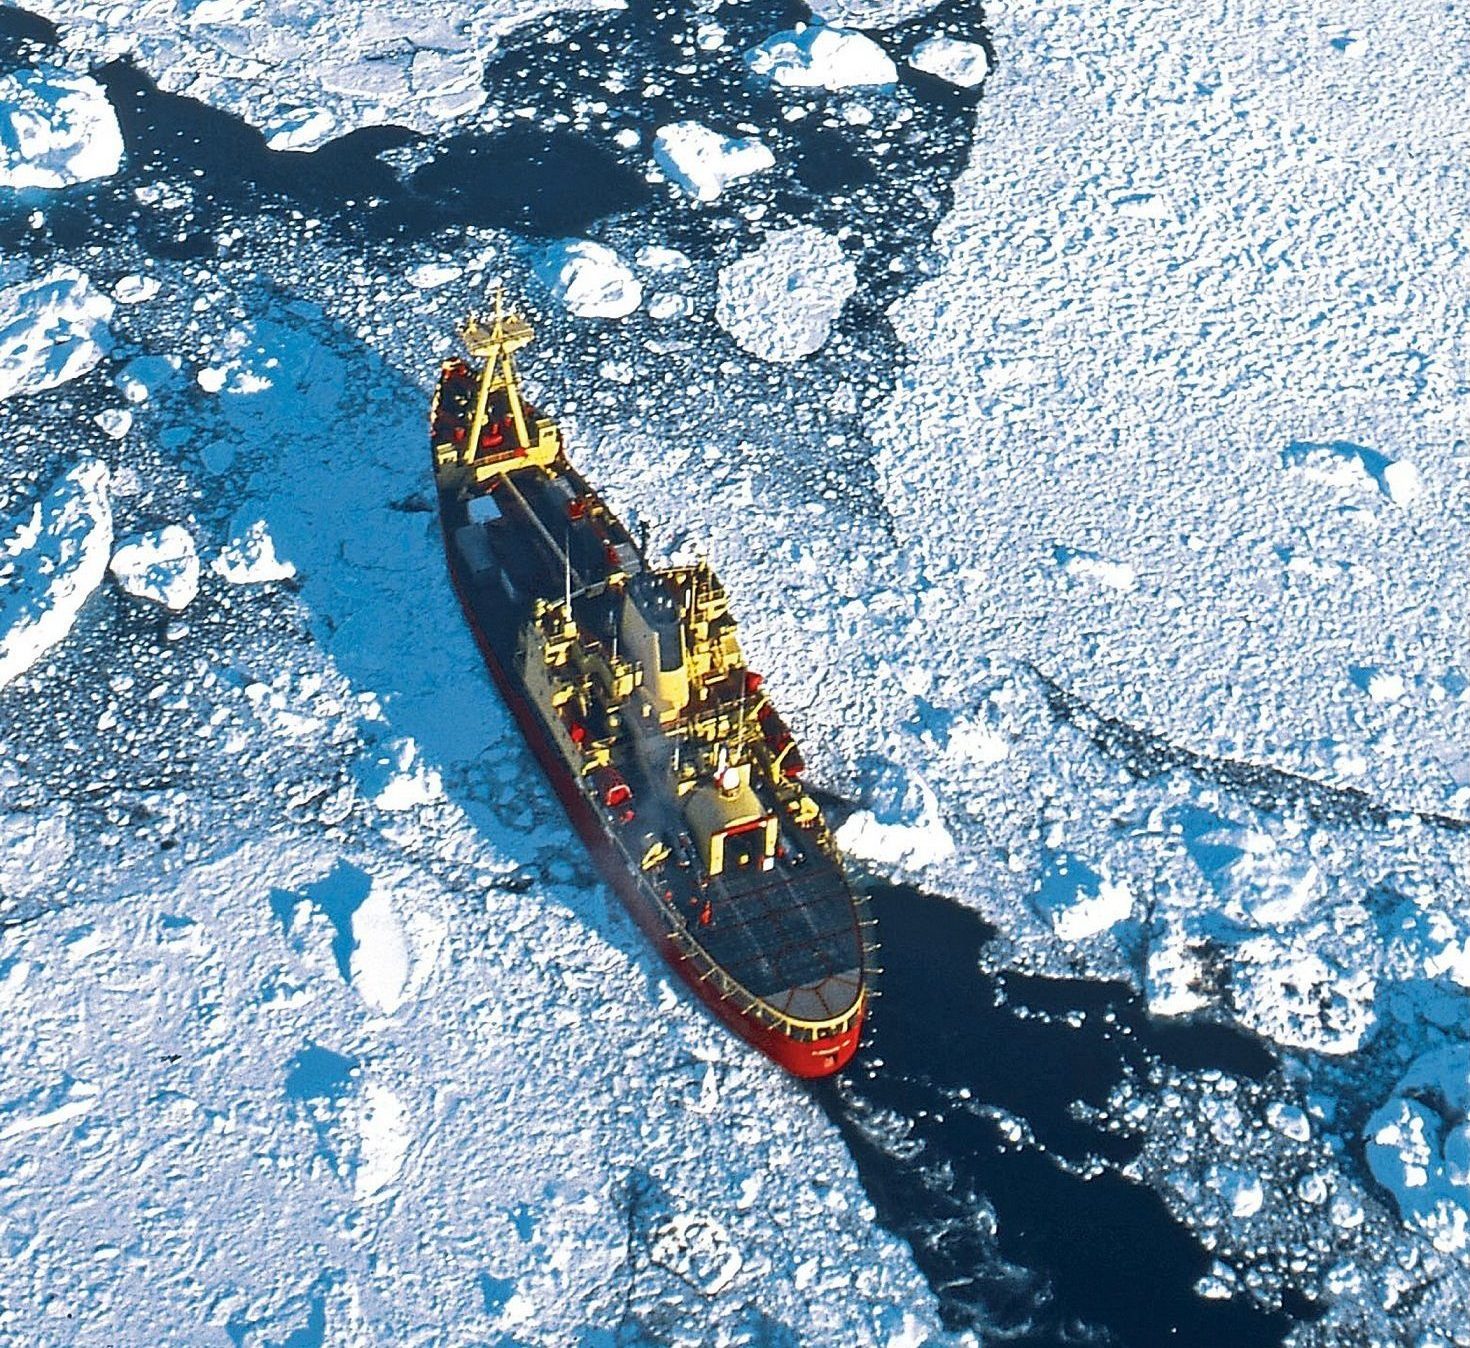
The Chilean icebreaker ‘Veil.’ (EFE/Chilean Navy)

Finally, it is worth stressing the general spirit of camaraderie in the Antarctic among South American navies. The PANC is a security-related initiative of two navies coming together in spite of historical differences and ongoing territorial claims in the Antarctic. Similarly, Uruguay has shared the results of some scientific studies with Chile and Argentina. In addition, Uruguay’s Mobile Marine Meteorological Station Project (Proyecto Estacion Meterologica Movil Marina) is an ongoing project that provides real-time information such as wind direction and speed, atmospheric and barometric pressure; and wave period, height, and type to Argentine and Chilean stations. This is a prime example of Latin American navies and scientific centers coming together to build upon each other’s successes in Antarctica.

Slow Improvements

While the aforementioned developments clearly demonstrate how Latin American navies are growing Antarctic capabilities, they should not be overestimated as there are also troubling shortcomings, particularly due to budget issues. For example, while Argentina’s icebreaker Irízar recently commenced sea trials and will likely return to operational duty by the 2017-2018 season, it has taken a decade-long reconstruction effort to repair the platform after it was ravaged by a fire in 2007. Similarly, budget issues have affected Argentina’s recent Antarctic operations, best exemplified by the recent summer 2016- 2017 season, in which the government had trouble figuring out how to resupply its Antarctic bases.

As for other nations, platforms that are too old to continue operating safely are eventually replaced by other vessels, which is not the same as expanding a fleet in terms of numbers. For example, Peru’s Carrasco will replace BIC Humboldt, which was constructed in the late 1970s and has gone through extensive overhauls to extend its operational life. Similarly, the new Chilean icebreaker will replace Viel, which was constructed in the late 1960s. Other naval platforms utilized for Antarctic operations, including the PANC, will soon become outdated. For example, Chile deployed ATF Lautaro (67) to the 2016-2017 PANC mission, a vessel constructed in 1973, while Argentina deployed ARA Islas Malvinas (A24), constructed in the 1980s. While replacement platforms are always welcome, expanding fleets by acquiring newly constructed ships would be more practical as their operational lives would last much longer than repurposed, older vessels.

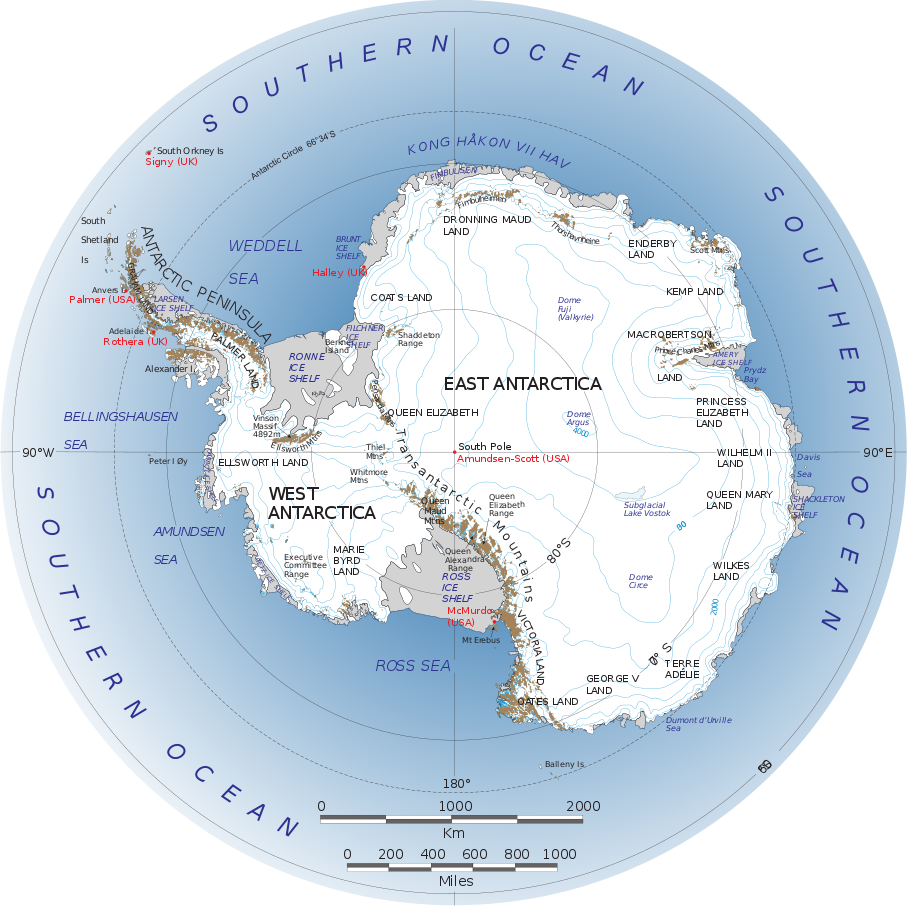
Map of Antarctica (NASA)

The aforementioned Argentine Almirante Irízar illustrates the benefits of a stronger commitment by regional states toward their Antarctic programs, including their naval platforms. While its post-fire reconstruction was extensive and lengthy, the Argentine government’s investment has made the vessel one of the 10 biggest icebreakers in the world, as well as one of the most capable. In a recent navigational test, the ship surpassed expectations, and showed no signs of the various previous problems it had when it first made its way to the Antarctic from Finland in 1978. Not only does the ship have improved navigation capabilities, but it is also now multipurpose, housing eight top-of-the-line scientific laboratories, and an overall scientific investigation sector six times larger than that of its original construction. Despite the lengthy timeline of the repair, the Argentine government’s decision to allocate scarce resources in revamping the Irizar is a Cinderella Story of sorts, as it exemplifies the benefits that could come from a bigger budget committed to Antarctic maritime operations. Obtaining a new vessel would have probably taken less time than repairing the Irizar, nevertheless, if reports are to be believed, this modernized vessel will be of great help for Argentina’s Antarctic operations for the foreseeable future.

Final Thoughts

Navies are usually viewed through the prism of defense and security; however they also play a critical role in Antarctic programs. Certainly other military services, government departments, and scientific institutions are other necessary pillars of any vibrant and robust Antarctic program, but navies are a sort of spearhead as they employ the primary platforms that deploy to this frozen continent. Hence it comes as no surprise that navies are prominently mentioned in the White Papers of several regional countries regarding Antarctic operations as they are engaged in various operations ranging from scientific activities to providing emergency assistance.

Countries like Peru and Chile are working on obtaining new platforms for Antarctic use while Colombia has refitted one of its navy’s vessels for these operations. Meanwhile, the Argentine and Chilean navies have come together to create a joint Antarctic naval patrol that has helped vessels and Antarctic bases in need. Finally, Uruguay’s scientific program and projects are also notable as they provide data that allows the multifaceted work of the Latin American countries in the region to continue operations safely and effectively.

The importance of Arctic and Antarctic geopolitics will increase due to climate change and the approaching year 2048, when the Antarctic Treaty is up for revision. The modernization of polar-capable vessels, such as Argentina’s Alimirante Irizar, if not the acquisition of newer ones like Peru’s Carrasco, will help Latin American navies increase the reliability and projection of already successful missions in Antarctica thereby fortifying Latin America’s presence and increasing its voice in regards to the future of the frozen continent.

For further info, see: “Reinvigorating Peru’s role in Antarctic geopolitics” (The Polar Journal, 2015) and “Argentina, Chile and the Joint Antarctic Naval Patrol: a successful confidence building mechanism” (The Polar Journal, 2017).

W. Alejandro Sanchez is a researcher who focuses on geopolitical, military, and cyber security issues in the Western Hemisphere. Follow him on Twitter: @W_Alex_Sanchez.

Brittney J. Figueroa is a recent graduate from the University of California, Santa Barbara with a Bachelors degree in Global Studies, and a Minor in Latin American Iberian Studies.

The views presented in this essay are the sole responsibility of the authors and do not necessarily reflect those of any institutions with which the authors are associated.

Featured Image: Chilean icebreaker in Brandy Bay, Antarctica. (Wikimedia Commons)

Beijing’s Views on Norms in Cyberspace and Cyber Warfare Strategy Pt. 1

By LCDR Jake Bebber USN

The following is a two-part series looking at PRC use of cyberspace operations in pursuit of its national strategies and the establishment of the Strategic Support Force. Part 1 considers the centrality of information operations and information war to the PRC’s approach toward its current struggle against the U.S. Part 2 looks at the PRC’s use of international norms and institutions in cyberspace, and possible U.S. responses.

Introduction

A recent article noted a marked shift in Chinese strategy a few short years ago which is only now being noticed. Newsweek author Jeff Stein wrote a passing reference to a CCP Politburo debate under the presidency of Hu Jintao in 2012 in which “Beijing’s leading economics and financial officials argued that China should avoid further antagonizing the United States, its top trading partner. But Beijing’s intelligence and military officials won the debate with arguments that China had arrived as a superpower and should pursue a more muscular campaign against the U.S.”1

The nature of this competition is slowly taking shape, and it is a much different struggle than the Cold War against the Soviet Union – however, with stakes no less important. This is a geoeconomic and geoinformational struggle. Both U.S. and PRC views on cyber warfare strategy, military cyber doctrine, and relevant norms and capabilities remain in the formative, conceptual, and empirical stages of understanding. There is an ongoing formulation of attempting to understand what cyberspace operations really are. While using similar language, each has different orientations and perspectives on cyberspace and information warfare, including limiting structures, which has led to different behaviors. However, the nature of cyberspace, from technological advancement and change, market shifts, evolving consumer preferences to inevitable compromises, means that while windows of opportunity will emerge, no one side should expect to enjoy permanent advantage. Thus, the term ‘struggle’ to capture the evolving U.S.-PRC competition.

The PRC recognized in the 1990s the centrality of information warfare and network operations to modern conflict. However, it has always understood the information space as blended and interrelated. Information is a strategic resource to be harvested and accumulated, while denied to the adversary. Information warfare supports all elements of comprehensive national power to include political warfare, legal warfare, diplomatic warfare, media warfare, economic warfare, and military warfare. It is critical to recognize that the PRC leverages the American system and its values legally (probably more so than illegally), to constrain the U.S. response, cloud American understanding, and co-opt key American institutions, allies, and assets. In many ways, the PRC approach being waged today is being hidden by their ability to work within and through our open liberal economic and political system, while supplemented with cyber-enabled covert action (such as the OPM hack).

To support their comprehensive campaign, the PRC is reforming and reorganizing the military wing of the Communist Party, the People’s Liberation Army (PLA), posturing it to fight and win in the information space. Most notably, it recently established the Strategic Support Force (SSF) as an umbrella entity for electronic, information, and cyber warfare. Critical for U.S. policymakers to understand is how the SSF will be integrated into the larger PLA force, how it will be employed in support of national and military objectives, and how it will be commanded and controlled. While much of this remains unanswered, some general observations can be made.

This reform postures the PLA to conduct “local wars under informationized conditions” in support of its historic mission to “secure dominance” in outer space and the electromagnetic domain. Network (or cyberspace) forces are now alongside electromagnetic, space, and psychological operations forces and better organized to conduct integrated operations jointly with air, land, and sea forces.2

This change presents an enormous challenge to the PLA. The establishment of the SSF disrupts traditional roles, relationships, and processes. It also disrupts power relationships within the PLA and between the PLA and the CCP. It challenges long-held organizational concepts, and is occurring in the midst of other landmark reforms, to include the establishment of new joint theater commands.3 However, if successful, it would improve information flows in support of joint operations and create a command and control organization that can develop standard operating procedures, tactics, techniques, procedures, advanced doctrine, associated training, along with driving research and development toward advanced capabilities.

While questions remain as to the exact composition of the Strategic Support Force, there seems to be some consensus that space, cyber, electronic warfare, and perhaps psychological operations forces will be centralized into a single “information warfare service.” Recent PLA writings indicate that network warfare forces will be charged with network attack and defense, space forces will focus on ISR and navigation, and electronic warfare forces will engage in jamming and disruption of adversary C4ISR. It seems likely that the PRC’s strategic information and intelligence support forces may fall under the new SSF. The PLA’s information warfare strategy calls for its information warfare forces to form into ad hoc “information operations groups” at the strategic, operational, and tactical levels, and the establishment of the SSF will save time and enable better coordination and integration into joint forces. The SSF will be better postured to conduct intelligence preparation of the battlespace, war readiness and comprehensive planning for “information dominance.”4

The establishment of the SSF creates a form of information “defense in depth,” both for the PLA and Chinese society as a whole. The SSF enables the PLA to provide the CCP with “overlapping measures of electronic, psychological, and political deterrents.” It is reasonable to expect that there will be extensive coordination and cooperation among the PRC’s military, internal security, network security, “commercial” enterprises such as Huawei and ZTE, political party organizations, state controlled media both inside and outside China, and perhaps even mobilization of Chinese populations.

Chinese Information Warfare Concepts and Applications

Recent Chinese military writings have stressed the centrality of information to modern war and modern military operations. Paying close attention to the way the West – principally the U.S. – conducted the First Gulf War and operations in Kosovo and the Balkans in the 1990s, the PRC has been aggressively pursuing a modernization and reform program that has culminated in where they are today. Indeed, there is close resemblance to PLA and PRC aspirational writing from the 1990s to today’s force structure.

In many ways, the PLA understanding of modern war reflects the American understanding in so much as both refer to the centrality of information and the need to control the “network domain.” “Informatized War” and “Informatized Operations” occur within a multi-dimensional space – land, sea, air, space and the “network electromagnetic” or what Americans generally understand as “cyberspace.” The U.S. has long held that the control of the network domain provides a significant “first mover advantage,” and the PRC is well on the way toward building the capability for contesting control of the network domain. Its writings consistently hold that the PLA must degrade and destroy the adversary’s information support infrastructure to lessen its ability to respond or retaliate. This is especially necessary for “the weak to defeat the strong,” because most current writing still suggests that the PLA believes itself still inferior to American forces, though this perception is rapidly changing. Regardless, the PRC understanding of modern war supposes a strong incentive for aggressive action in the network domain immediately prior to the onset of hostilities.6 These operations are not restricted geographically, and we should expect to see full-scope network operations worldwide in pursuit of their interests, including in the American homeland.7

There are three components to a strategic first strike in the cyber domain. The first component is network reconnaissance to gain an understanding of critical adversary networks, identifying vulnerabilities, and manipulating adversary perception to obtain strategic advantage. Network forces are then postured to be able to conduct “system sabotage” at a time and place of the PRC’s choosing. When the time is right, such as a prelude to a Taiwan invasion or perhaps the establishment of an air defense identification zone over the South China Sea, the PRC will use system sabotage to render adversary information systems impotent, or to illuminate the adversary’s “strategic cyber geography” in order to establish a form of “offensive cyber deterrence.” The PRC could take action to expose its presence in critical government, military, or civilian networks and perhaps conduct some forms of attack in order to send a “warning shot across the bow” and give national decision-makers reason to pause and incentive to not intervene.8

Indeed, unlike the American perspective, which seeks to use cyberspace operations as a non-kinetic means to dissuade or deter potential adversaries in what Americans like to think of as “Phase 0,” the PLA has increasingly moved toward an operational construct that blends cyberspace operations with kinetic operations, creating a form of “cyber-kinetic strategic interaction.” The goal would be to blind, disrupt, or deceive adversary command and control and intelligence, surveillance, and reconnaissance (C4ISR) systems while almost simultaneously deploying its formidable conventional strike, ballistic missile, and maritime power projection forces. The PLA envisions this operational concept as “integrated network electronic warfare,” described by Michael Raska as the “coordinated use of cyber operations, electronic warfare, space control, and kinetic strikes designed to create ‘blind spots’ in an adversary’s C4ISR systems.”9 

The PLA has recently described this as a form of “network swarming attacks” and “multi-directional maneuvering attacks” conducted in all domains – space, cyberspace, ground, air, and sea. The Strategic Support Force has been designed to provide these integrated operations, employing electronic warfare, cyberspace operations, space and counter-space operations, military deception and psychological operations working jointly with long-range precision strike, ballistic missile forces and traditional conventional forces.

Essential to these concepts are China’s ability to achieve dominance over space-based information assets. PRC authors acknowledge this as critical to conducting joint operations and sustaining battlefield initiative. This includes not only the orbiting systems, but ground stations, tracking and telemetry control, and associated data systems. We can expect full-scope operations targeting all elements of America’s space-based information system enterprise.

Important to all of this is the necessity of preparatory operations that take place during “peacetime.” China understands that many of its cyberspace, network, electronic and space warfare capabilities will not be available unless it has gained access to and conducted extensive reconnaissance of key systems and pre-placed capabilities to achieve desired effects. We should expect that the PRC is actively attempting to penetrate and exploit key systems now in order to be able to deliver effects at a later date.

Chinese Understandings of Deterrence and International Law in Cyber Warfare

China recently released the “International Strategy of Cooperation on Cyberspace.”10 Graham Webster at the Yale Law School made some recent observations. First, it emphasizes “internet sovereignty,” which is unsurprising, since the CCP has a vested interest in strictly controlling the information space within China, and between China and the rest of the world.  This concept of “internet sovereignty” should best be understood as the primacy of Chinese interests. China would consider threatening information sources outside of the political borders of China as legitimate targets for cyber exploitation and attack. In the minds of the CCP, the governance of cyberspace should recognize the sovereignty of states, so long as the Chinese state’s sovereignty is paramount over the rest of the world’s.

Second, the strategy suggests that “[t]he tendency of militarization and deterrence buildup in cyberspace is not conducive to international security and strategic mutual trust.” This appears to be aimed squarely at the U.S., most likely the result of Edward Snowden’s actions. The U.S. seems to also be the target when the strategy refers to “interference in other countries’ internal affairs by abusing ICT and massive cyber surveillance activities,” and that “no country should pursue cyber hegemony.” Of course, the PRC has been shown to be one of the biggest sources of cyber-enabled intellectual property theft and exploitation, and China’s cyber surveillance and control regimes are legendary in scope. Immediately after decrying the “militarization” of cyberspace, the strategy calls for China to “expedite the development of a cyber force and enhance capabilities … to prevent major crisis, safeguard cyberspace security, and maintain national security and social stability.” These broad, sweeping terms would permit China to later claim that much of its activities that appear to violate its own stated principles in the strategy are indeed legitimate.

The strategy seeks to encourage a move away from multi-stakeholder governance of the Internet to multilateral decision-making among governments, preferably under the United Nations. This would certainly be in China’s interests, as China continues to hold great sway in the U.N., especially among the developing world. After all, China is rapidly expanding its geoeconomic and geoinformational programs, leveraging its state-owned enterprises to provide funding, resources, and informational infrastructure throughout Africa, Asia, Europe, and the Americas. As more countries become dependent on Chinese financing, development, and infrastructure, they will find it harder to oppose or object to governance regimes that favor Chinese interests.

Naturally, the strategy emphasizes domestic initiatives and a commitment to a strong, domestic high-tech industry. This would include the “Made in China 2025” plan, which has received a great deal of attention. The plan seeks to comprehensively upgrade and reform Chinese industry, with an emphasis on information technology.11

When considering deterrence in the Chinese understanding, it is important to remember that China approaches it from a different context than the United States. Jacqueline Deal noted that China’s basic outlook proceeds from the premise that the “natural state of world is one of conflict and competition, and the goal of strategy is to impose order through hierarchy.”12 While Americans understand deterrence as a rational calculation, the Chinese approach emphasizes the conscious manipulation of perceptions.

Indeed, the Chinese term weishe, which translates as “deterrence,” also embodies the idea of “coercion.” We might see examples of this understanding by China’s historic use of “teaching a lesson” to lesser powers. In the 20th Century, Chinese offensives against India and Vietnam – thought by many in the West to be an example of tragic misunderstanding and failed signaling of core interests – might be better thought of as attempts by China to secure its “rightful” place atop the regional hierarchy. It is a form of “lesson teaching” that has long-term deterrent effects down the road.

We can expect therefore that cyberspace would become one means among many that China will use in support of its “Three Warfares” (public opinion, media, legal) concept in support of its larger deterrent or compellence strategies. It will likely be much broader than the use of PLA SSF forces, and could include cyber-enabled economic strategies, financial leverage, and resource withholding.

LCDR Jake Bebber is a cryptologic warfare officer assigned to the staff of Carrier Strike Group 12. He previously served on the staff of U.S. Cyber Command from 2013 – 2017. LCDR Bebber holds a Ph.D. in public policy. He welcomes your comments at: jbebber@gmail.com. These views are his alone and do not necessarily represent any U.S. government department or agency.

1. Available at: http://www.newsweek.com/cia-chinese-moles-beijing-spies-577442

2. Dean Cheng (2017). Cyber Dragon: Inside China’s Information Warfare and Cyber Operations. Praeger Security International.

3. Cheng 2017.

4. John Costello and Peter Mattis (2016). “Electronic Warfare and the Renaissance of Chinese Information Operations.” in China’s Evolving Military Strategy (Joe McReynolds, editor). The Jamestown Foundation.

6. Joe McReynolds, et. Al. (2015) “TERMINE ELECTRON: Chinese Military Computer Network Warfare Theory and Practice.” Center for Intelligence Research and Analysis

7.  Barry D. Watts (2014) “Countering Enemy Informationized Operations in Peace and War.” Center for Strategic and Budgetary Assessments

8. Timothy L. Thomas (2013) “China’s Cyber Incursions.” Foreign Military Studies Office

9. See: http://www.atimes.com/article/chinas-evolving-cyber-warfare-strategies/

10. See: http://news.xinhuanet.com/english/china/2017-03/01/c_136094371.htm

11. See: https://www.csis.org/analysis/made-china-2025

12. Jacqueline N. Deal (2014). “Chinese Concepts of Deterrence and their Practical Implications for the United States.” Long Term Strategy Group.

Featured Image: The Center for Nanoscale Materials at the Advanced Photon Source. (Photo: Argonne National Laboratory)